
PatientLock
VitalSec platform

Turn security evidence into verified action.

VitalSec connects the security tools already in your environment into one operating loop: current state, AI-assisted prioritization, customer-authorized remediation, post-change verification, cryptographic proof, and measurable risk direction.

Find cyber risk. Fix it. Prove it.

Inside VitalSec

See what needs attention.

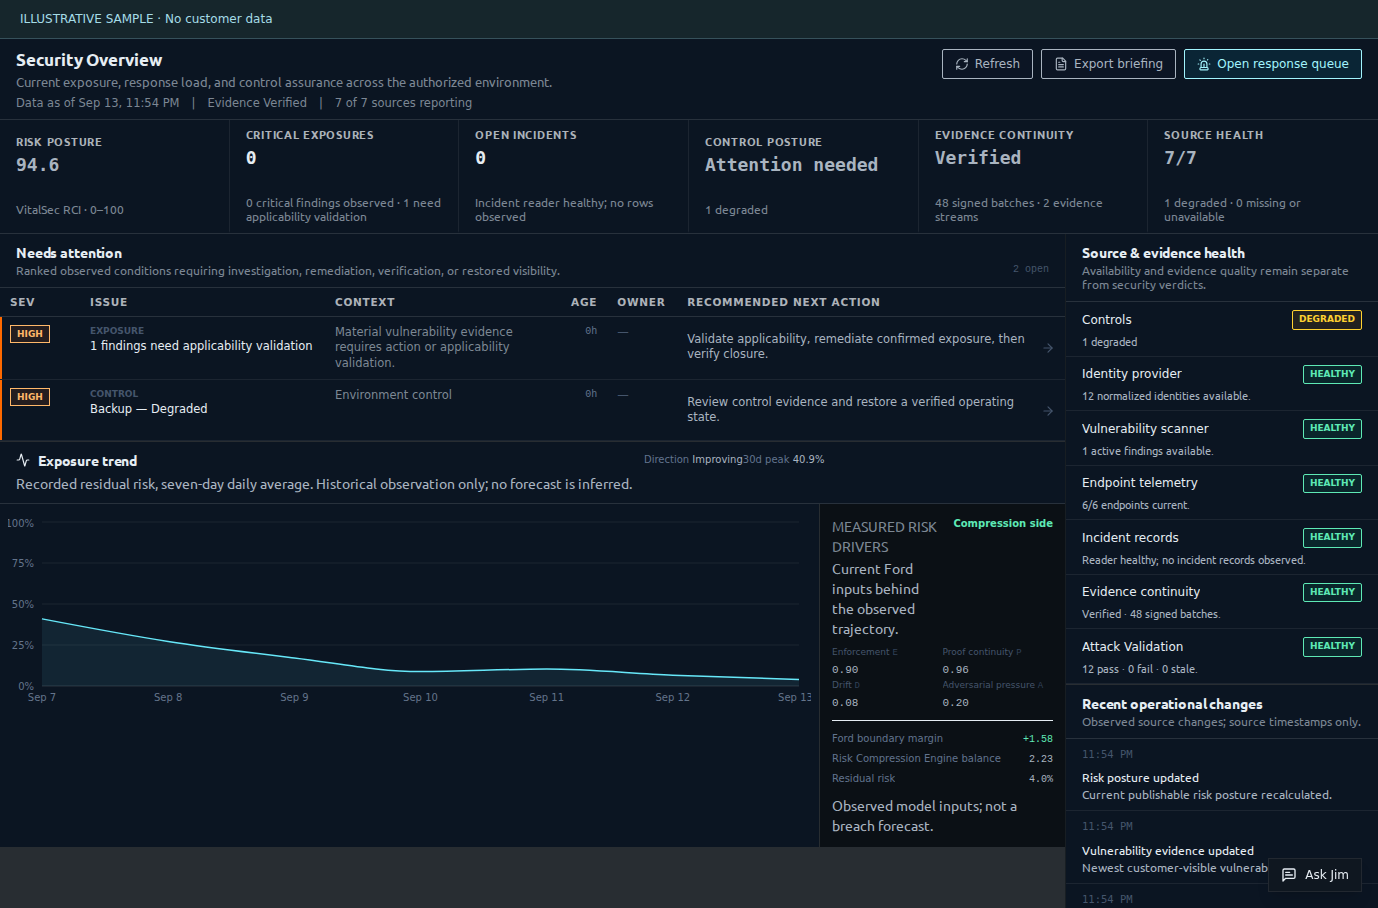
The Risk Compression Index, control health, exposure trends, and the evidence behind them in one operating view.

Sample VitalSec Overview with Risk Compression Index 94.6, a declining exposure trend, a degraded backup control, and source evidence health.
VitalSec Overview · Sample data

AI-native by design

AI reasons across the platform. Evidence and customer authority stay in control.

VitalSec uses AI to correlate signals, prioritize work, surface patterns, and explain change across the environment. AI does not replace authorization, source evidence, post-change validation, or the Ford Model.

The operating architecture

One loop, not six disconnected tools.

Observe → Decide → Act → Validate → Prove → Measure. VitalSec keeps the original finding, the decision, the approved change, the post-change validation, the evidence, the signed proof, and the risk measurement together so you can see what actually happened.

EndpointsIdentityVulnerabilityCloudNetworkSecurity tools
CustomerPortfolioMSP / MSSPBrokerCarrierReinsurer
  1. 01

    Observe

    See what is actually happening now using Rusty and connected systems.

  2. 02

    Decide

    Compare what is happening with what should be true and prioritize what matters.

  3. 03

    Act

    Run or route an approved fix.

  4. 04

    Validate

    Check the environment again and confirm whether the fix worked.

  5. 05

    Prove

    Keep the evidence of what was found, what changed, and what happened afterward.

  6. 06

    Measure

    Recalculate risk direction from validated evidence and show the movement.

Your team sets the limits.

The customer decides what can change
Credentials, permissions, target scope, delegated access, and remediation rights stay explicit.
Customer environments stay separate
Tenant and role controls keep one organization's evidence and actions separate from another's.
Automation stays inside approved limits
Automated work follows approved recipes, policy, target scope, kill switches, and execution permissions.
The result is checked after the action
VitalSec uses evidence observed after the action to determine whether the required state was restored.

Core platform machinery

Capabilities that put the control loop to work.

Rusty observes and acts at the endpoint. VUMA closes vulnerability work. CAAT tests whether controls hold. Evidence Continuity preserves the proof. Identity Authority connects access context, and ShadowAI brings AI use into the same governed work.

Endpoint observation & action

VitalSec endpoint agent family

Rusty

Rusty spans Windows, macOS, Linux, iOS, and Android. On desktop and server systems it observes device state, software and control health, carries out customer-approved endpoint actions, and reads the device again afterward. Rusty Mobile extends signed device identity, observation, heartbeat, and proof to iOS and Android, with management actions flowing through the customer's MDM or UEM.

Explore Rusty
Remediation & validated closure

Vulnerability remediation + validated closure

VUMA

Takes vulnerability findings from detection through the fix and the follow-up check. VUMA determines which findings actually apply, puts the important work first, applies supported fixes automatically when the customer has already approved them, retests the source, and keeps the evidence showing whether the problem was resolved.

Explore VUMA
Approved control testing

Continuous Automated Adversarial Testing

CAAT

Runs controlled, customer-approved adversarial tests against security controls and exposed paths. CAAT records PASS, FAIL, or INCONCLUSIVE from the observed evidence and keeps each test inside customer-set scope and safety boundaries.

Explore CAAT
Evidence & attestation

Continuous evidence + post-quantum attestation

Evidence Continuity

Turns platform operations into source-linked, tamper-evident proof. Evidence Continuity preserves provenance, actions, retests, observed results, Merkle integrity, signed attestations, and a live FIPS 204 ML-DSA-65 post-quantum co-attestation path.

Explore Evidence Continuity
Identity & access context

Identities, privileges & access

Identity Authority

Designed to connect identities, groups, privileged roles, applications, OAuth grants, and access changes to the same evidence and enforcement loop.

Explore Identity Authority
AI discovery & governance

AI use, policy & follow-up

ShadowAI

Discovers AI use and connects it to identity, policy, sanction, and data-egress context, with evidence for the decision and follow-up action.

Explore ShadowAI

Measurement & reporting

Understand the change. Carry the evidence forward.

The engine explains risk direction. The index summarizes the current measure. Reports carry the supporting evidence into review.

Risk direction + current measure

The engine

Risk Compression Engine

Models risk direction from current evidence and keeps the drivers behind a material change available for review.

Explore Risk Compression Engine

The index

Risk Compression Index

A normalized 0–100 operational measure, published when the evidence required to support it is complete and current.

Explore Risk Compression Index
Evidence for review

From operations to the people reviewing them

Reporting & Audit Packs

Current evidence, remediation history, validation, and risk movement in reusable audit, compliance, executive, and insurance-ready reporting.

Explore Reporting & Audit Packs

Evidence beyond the security team

Current proof, carried into insurance decisions.

Broker, carrier, and reinsurer workspaces organize VitalSec around each role. RiskBid and Claims Operations carry evidence between the parties involved.

Book & client readiness

Broker Workspace

Portfolio and client views, renewal readiness, evidence packages, market activity, and claims support.

Explore Broker Workspace

Underwriting & policy review

Carrier Workspace

Authorized opportunities, evidence review, responses, quotes, policy state, and material change.

Explore Carrier Workspace

Portfolio & concentration

Reinsurer Workspace

Shared dependencies, evidence quality, incidents, and portfolio signals across carriers and programs.

Explore Reinsurer Workspace

Workspace access determines what each role can see and do. It does not grant authority over the insured’s systems.

RiskBid

Current evidence accompanies market listings, selected-carrier review, responses, quotes, and the bound policy.

Explore RiskBid

Claims Operations

Incident and policy context stay attached to the sealed evidence bundle, carrier delivery, and receipt.

Explore Claims Operations
See the insurance operating model

The Ford Model

Understand the current state and how it changes.

Working controls and current proof push modeled risk down. Drift, stale evidence, and adversarial pressure push it up. VitalSec shows which side is winning, what changed, and the evidence behind the answer.

The Risk Compression Index summarizes the current measured security state. Exposure trends show how observed exposure changes over time. The Ford Model relates risk direction to Enforcement, Proof Continuity, Decay, and Adversarial Pressure.

dR/dt = f(E + P − D − A)

E — Enforcement

Controls that are active and restored when they drift.

P — Proof

Current evidence that supports the condition and the change.

D — Decay

Drift, staleness, and operational change that weaken confidence.

A — Adversarial pressure

Attackers and exploitable paths pressing against the environment.

Modeled risk compresses when E + P > D + A.

Who uses it

The same current evidence, organized for the decision each team has to make.

Healthcare

Run security, compliance, remediation, audit readiness, and proof from the same current evidence.

MSPs and MSSPs

Work across customers with clear customer permissions, separate evidence, and measurable results.

Private equity

Compare portfolio companies, establish a Day 0 baseline, drive 100-day plans, and prove improvement.

Brokers and carriers

Use current control evidence in renewal, underwriting, portfolio, and claims decisions.

Start with the security stack you already have.

VitalSec connects the findings, approved changes, validation, evidence, proof, and risk measurement that your existing tools leave scattered across separate systems.